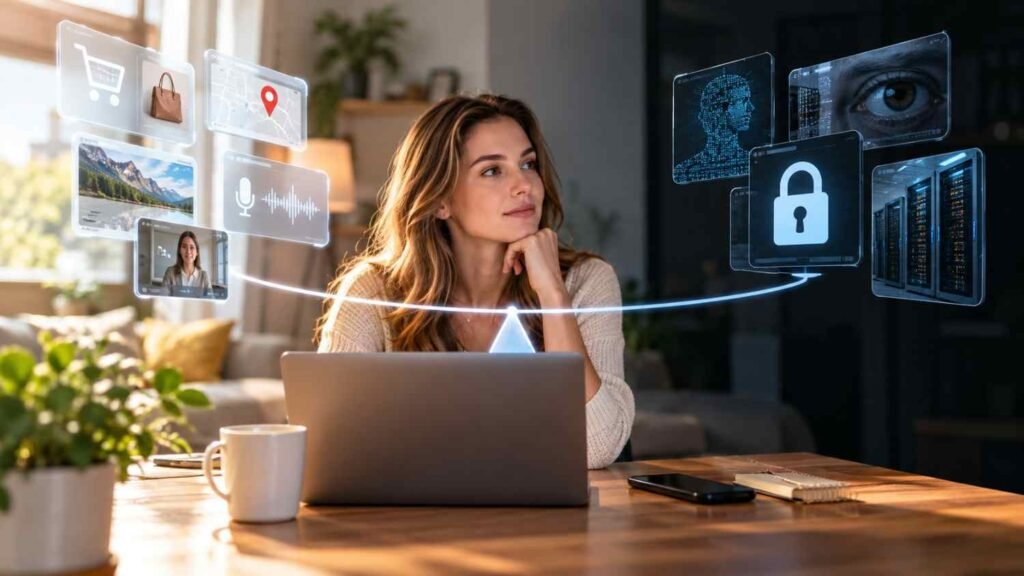
I’ve started noticing how casually AI tools have slipped into ordinary routines. I can ask a chatbot to tidy an email, explain a confusing bill, or compare products in seconds. The convenience feels real, especially when I’m busy, but each request also raises a question: what information am I handing over to get that useful answer?
I’ve also learned that privacy is not simply a matter of avoiding suspicious websites. A familiar app can still collect information, keep conversations, or connect details in ways I may not expect. AI privacy and data protection mean understanding those choices before sharing personal details, then deciding which conveniences are worth the trade-off.
Why Convenience Can Come With a Privacy Cost
AI systems often work by finding patterns across large amounts of information. Recommendation engines use activity to suggest products, while assistants process prompts. More context can make results relevant, but it may include names, locations, routines, and details about other people.
The concern is not that every AI service misuses information. The problem is that data practices differ. Some services retain prompts, offer model-improvement controls, or set different terms for business accounts. Read the privacy policy and settings instead of guessing. Compare providers before trusting one with sensitive tasks. Clear choices help users set reasonable limits for your own peace of mind.
What Happens to Information You Share?
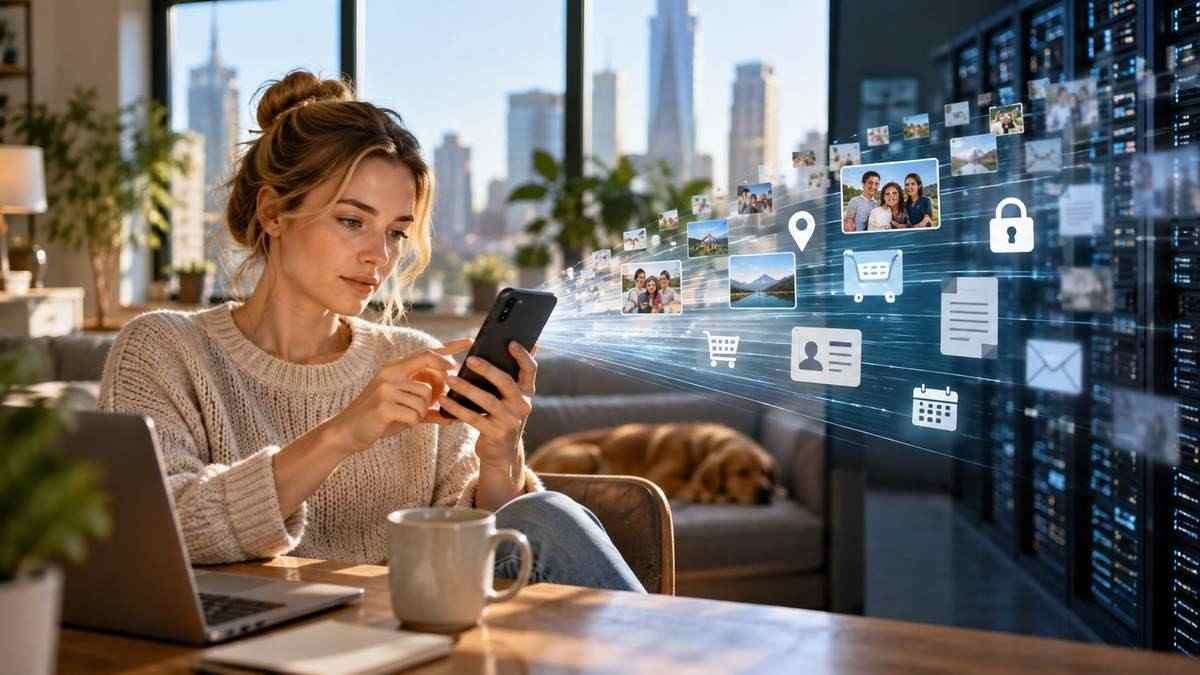
A prompt does not always disappear when an answer appears. Pause before sharing. Depending on the service, prompts, files, account details, and usage data may be stored for safety, troubleshooting, improvement, or training. These purposes differ, so check them separately. For workplace tools, confirm the organization’s agreement and administrator settings before sharing internal information.
For example, asking an assistant to rewrite a résumé may expose a phone number, employment history, and home address. Uploading a tax document could reveal income, account details, or a Social Security number. Remove identifying details first and share only what the tool needs.
Data can also reveal more than a person deliberately shares. AI may connect public posts, browsing behavior, purchase patterns, or other available details to infer sensitive traits. Removing a name does not always make a dataset anonymous if enough clues remain. Some models may reproduce training fragments, though risks and safeguards vary. Users should understand the service’s policies and avoid treating a chatbot as a confidential diary, lawyer, or health professional.
Good digital organization helps, too. Knowing how to organize browser bookmarks makes it easier to keep official privacy pages, account settings, and trusted security resources close at hand instead of searching hurriedly when something goes wrong. Remove outdated links that lead to old settings or advice.
Practical Ways to Reduce Exposure
Start with the information itself. Do not paste passwords, authentication codes, private medical records, confidential client files, or complete financial documents into a general-purpose AI tool. Replace names and account numbers with placeholders, summarize the situation, or use fictional figures.
Next, review the service’s data controls. Look for options governing chat history, model improvement, temporary conversations, deletion, and connected apps. Settings differ: turning off training may not erase chats, and deleting a conversation may not remove every backup. Incognito browsing does not change a service’s retention practices.
Protect the account as carefully as the content. Use a unique password, enable multifactor authentication, install updates, and review extensions with file access. Remove unused connections and follow your employer’s approved tools for sensitive work.
Make Privacy Part of Everyday Digital Habits
Small routines can make safer choices easier. Before submitting a prompt, ask whether each detail is necessary. Avoid sharing other people’s information without permission, and use generic examples when possible.
A broader routine matters just as much. Building technology habits for digital wellbeing can mean setting limits on unnecessary app permissions, checking privacy controls every few months, and thinking before connecting another service. They reduce careless sharing and make privacy decisions manageable.
What Companies and Policymakers Can Do
Responsibility should not fall entirely on individual users. Privacy by design means building protections into a product from the start, collecting only necessary information, limiting access, and explaining data practices in plain language. Federated learning can keep some training data on local devices, while differential privacy adds noise to protect individuals in aggregate analysis. Neither guarantees privacy.
In the United States, protections depend on the type of data, service, and applicable state or federal rules. The Federal Trade Commission can act against deceptive privacy promises, and state laws add requirements. The EU’s GDPR and AI Act are relevant internationally but do not automatically apply to every US user: clear disclosures and oversight matter. Organizations can assess systems before launch and restrict employee access.
FAQs: AI Privacy and Data Protection: Balancing Convenience and Personal Privacy
1. What does AI privacy and data protection mean?
It refers to practices that govern how AI systems collect, process, store, share, and protect personal information. It includes both technical safeguards and clear rules about how data may be used.
2. Can AI chatbots use my conversations for training?
Some services may use conversations to improve models, depending on the product, account type, and settings. Review the provider’s current policy and controls rather than assuming every chatbot works the same way. Some services offer account-level opt-outs, while others provide different protections through paid or workplace plans. Recheck settings after major product updates.
3. What information should I avoid sharing with AI?
Avoid passwords, verification codes, Social Security numbers, private health records, confidential work files, and full financial documents. Remove identifying details when possible.
4. Does private browsing make AI chats private?
No. Private browsing mainly limits what your browser saves locally. It does not automatically change what an AI provider collects, stores, or uses. Review the service’s own privacy settings and terms. If the information is sensitive, avoid submitting it until you understand the provider’s retention and access rules. When unsure, leave it out.
Keeping Convenience Without Giving Up Control
AI can save time and make digital services more useful, and avoiding it altogether is not the only sensible response. The better approach is to match the tool to the task: use general assistants for low-risk questions, keep sensitive records out of unnecessary prompts, and check how a service handles information before trusting it with more. Convenience becomes easier to enjoy when the boundaries are deliberate.
Privacy is rarely one dramatic decision. It is a series of small choices about what to share, what to connect, and what to question. A few seconds of caution can preserve options later.